New Jersey Public Sector Cybersecurity Summit 2026
Overview
The New Jersey Public Sector Cybersecurity Summit is where government defends the future.
This public sector-focused event brings together IT security leaders, risk managers, and public officials to tackle the evolving cyber threats facing state and local government. Through expert-led sessions, peer exchange, and real-world case studies, attendees gain practical strategies to strengthen cyber resilience, protect critical infrastructure, and lead with confidence in an age of constant risk. Designed specifically for the public sector, this summit delivers insights you can act on and alliances you can trust!
In partnership with:

Speakers
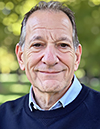
Doug Cassle

AI Architect, Prompt Security (a SentenialOne company)
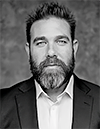
John DeGood
Senior Lecturer, Department of Computer Science, The College of New Jersey




Agenda
Thursday, October 8 |
|
8:00 AM Eastern |
Registration and Morning Refreshments in the Exhibit Area |
9:00 AM Eastern |
Pledge of Allegiance |
9:02 AM Eastern |
Welcome |
9:05 AM Eastern |
Open Remarks and State of the StateMichael Geraghty, Director, New Jersey Cybersecurity and Communications Integration Cell and Chief Information Officer, State of New Jersey |
9:30 AM Eastern |
Keynote - Securing Your Agentic Workforce: From Blind Trust to Zero TrustWe have been calling AI a coworker, a teammate, a copilot — even a friend. That language is not just imprecise. It is a security failure. When you frame AI as a colleague, you issue it credentials like a colleague, extend it trust like a colleague, and audit it like furniture instead of governing it like the non-human identity it actually is. In this high-energy, provocative keynote, Noelle maps the contractor lifecycle directly to the three autonomy levels of responsible AI: Human in the Loop, Human on the Loop, and the governance trap most organizations fall into when they try to go fully autonomous. She introduces the concept of the Sponsor field as the accountability mechanism that never disappears, no matter how much autonomy an agent earns. Audiences leave with a five-step Agent Onboarding checklist, a maturity ladder they can place their organization immediately, and one insight that reframes everything: you can increase the autonomy. You cannot outsource responsibility. Noelle Russell, Founder & Chief AI Officer, AI Leadership Institute |
10:10 AM Eastern |
Networking Break in the Exhibit Area |
10:40 AM Eastern |
General Session – Visibility, Control and Cyber Resilience in an AI-Driven WorldAs cyber threats continue to evolve and IT environments become increasingly complex, government agencies must strengthen visibility, improve control, and build resilient security program s that can adapt to an AI-driven threat landscape. Join public-sector cybersecurity leaders as they discuss practical strategies for improving enterprise-wide visibility, securing identities, modernizing security operations, and leveraging AI to enhance detection, accelerate response, and strengthen governance and compliance. Moderator: Brian Cohen, Vice President, Center for Digital Government Doug Cassle, AI Architect, Prompt Security (a SentenialOne company) Lee Micai, Chief Technology Officer, Office of Information Technology, Mercer County |
11:20 AM Eastern |
General Session – Threat Hunting in Action: Staying Ahead of Today’s AdversariesCyber threats are becoming faster, more sophisticated, and increasingly difficult to detect using traditional security approaches. Rather than waiting for alerts, leading government organizations are adopting proactive threat hunting strategies to uncover hidden threats, validate defenses, and stop attacks before they escalate. In this session, we'll examine how government agencies are shifting from reactive security to proactive threat hunting by leveraging AI, behavioral analytics, and threat intelligence to proactively identify hidden threats, validate defenses, and stay ahead of increasingly sophisticated adversaries. Moderator: Ken Skeen, Conference Director of New York and New Jersey Programs and Events, Government Technology John DeGood, Senior Lecturer, Department of Computer Science, The College of New Jersey |
12:00 PM Eastern |
Lunch |
1:00 PM Eastern |
Short BreakPlease proceed to the general session. |
1:10 PM Eastern |
General Session – Asset Intelligence: Reducing Exposure and Strengthening Cyber ResilienceA strong cybersecurity program begins with knowing exactly what exists across the enterprise. Yet many government organizations continue to struggle with incomplete asset inventories, unmanaged devices, software sprawl, and expanding attack surfaces that increase operational risk. In this session, we'll explore how public-sector organizations are improving cyber resilience through greater asset intelligence, continuous visibility, exposure management, and proactive cyber hygiene. Learn how agencies are identifying unknown assets, prioritizing vulnerabilities, strengthening endpoint management, and reducing cyber risk through better visibility and continuous exposure management. Moderator: Robert McQueen, Chief Technology Officer, Township of Hamilto David Fenton, Director, NJMedex Platform, Department of Health, State of New Jersey |
1:50 PM Eastern |
General Session – AI vs. AI: Securing Government in the Age of Intelligent ThreatsArtificial intelligence is reshaping the cybersecurity landscape at an unprecedented pace. While government agencies are leveraging AI to strengthen cyber defenses, improve decision-making, and increase operational efficiency, adversaries are using the same technologies to launch faster, more sophisticated attacks—from AI-generated phishing and deepfakes to automated malware and autonomous reconnaissance. Join this conversation as government cybersecurity leaders discuss how agencies can responsibly harness the power of AI while balancing innovation with governance, security, and public trust. Moderator: Marc Pfeiffer, Associate Director, Bloustein Local, Center for Urban Policy Research, Rutgers University Sam Kinch, Solution Engineer, Tanium |
2:30 PM Eastern |
Networking Break in the Exhibit Area |
2:50 PM Eastern |
General Session – Cyber Crisis Live: Responding to a Government Ransomware AttackA cyberattack can unfold in minutes, forcing leaders to make critical decisions under pressure with limited information. How prepared is your organization? Join this interactive closing session as public-sector cybersecurity leaders guide attendees through a realistic ransomware attack affecting a New Jersey government organization. As the scenario unfolds, panelists will discuss the decisions they would make, the tradeoffs they would consider, and the lessons they've learned from responding to real-world cyber incidents. Audience members will participate through live polling and scenario-based decision points, exploring how to contain the attack, coordinate response efforts, communicate with stakeholders, and restore critical services. Stan Field, CFE, MA, Cybersecurity State Coordinator, CISA Region 2, Cybersecurity and Infrastructure Security Agency |
3:30 PM Eastern |
End of ConferenceConference times, agenda, and speakers are subject to change. |
The War Memorial
1 Memorial Drive
Trenton, NJ 08608
(609) 984-8484
The War Memorial



Registration Information / Contact Us
Event Date: October 8, 2026
Open to Public Sector only.
Registration - Free
If you represent a Private Sector organization and are interested in Sponsorship Opportunities, please contact Heather Earney.
This event is open to all individuals who meet the eligibility criteria, without regard to race, color, religion, gender, gender identity, age, disability, or any other protected class. We are committed to fostering an inclusive and welcoming environment for all participants.
Contact Information
Need help registering, or have general event questions? Contact:
Lee Vang
Government Technology
A division of e.Republic
Phone: (916) 932-1407
E-mail: lvang@erepublic.com
Already a sponsor, but need a hand? Reach out to:
Mireya Gaton
Government Technology
A division of e.Republic
Phone:(916) 296-2617
E-Mail: mgaton@erepublic.com
Want to sponsor and stand out? Reach out to explore opportunities!
Heather Earney
Government Technology
A division of e.Republic
Phone: (916) 365-2308
E-mail: heather.earney@erepublic.com